

Someone Is Scanning for Your MCP Servers and AI Assistant Credentials, (Mon, Jul 13th)
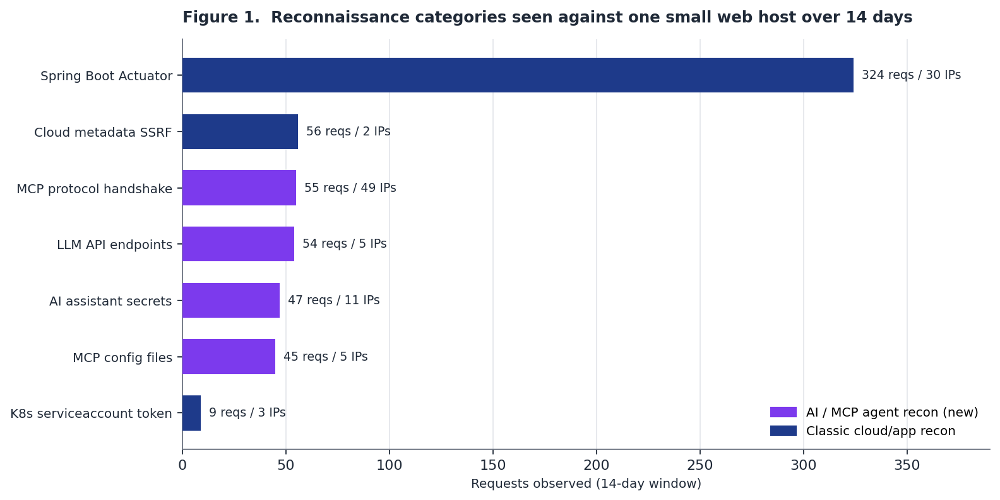
A SANS Internet Storm Center analysis reveals a widespread scanning campaign targeting servers to identify and exploit vulnerabilities related to AI assistants and local Large Language Models (LLMs). The scans are actively seeking exposed Model Context Protocol (MCP) servers, AI assistant configuration files, and unauthenticated LLM endpoints. The campaign demonstrates a proactive approach by threat actors who are already anticipating the deployment of AI agent tooling and are aggressively harvesting credentials and access points. Defenders should immediately check their logs for MCP handshakes, AI-config paths, and exposed LLM endpoints, and implement protections like blocking MCP requests and metadata service protection.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data