Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
A use-after-free vulnerability in the Linux kernel's AF_UNIX socket subsystem allows an attacker to escape a container and gain root access on the host.
13 article(s) in our index mention this organisation.
A use-after-free vulnerability in the Linux kernel's AF_UNIX socket subsystem allows an attacker to escape a container and gain root access on the host.
Researchers have discovered a new hardware attack, DDRop, that breaks the memory protection offered by Intel TDX and AMD SEV-SNP, two key technologies used in cloud computing to protect customer data. The attack involves…
Australian authorities have charged two men linked to the cybercrime group TeamPCP, allegedly responsible for a widespread supply chain attack targeting over 1,000 organizations globally. The group exploited compromised…
The ShinyHunters group is aggressively targeting numerous companies, including Logitech and Streamlabs, using a coordinated extortion campaign. They claim to have compromised vast amounts of sensitive data – including pe…
A group of Russian threat actors are exploiting vulnerabilities in Microsoft's on-prem SharePoint to steal corporate data. The attackers are impersonating Signal support to carry out phishing attacks, leveraging a zero-d…
A critical vulnerability in SAP Commerce Cloud was rapidly exploited by hackers just days after its public announcement. The flaw, tracked as CVE-2026-58231, allows for arbitrary code execution and poses a significant ri…
A research firm, Silent Push, demonstrated how artificial intelligence can significantly amplify the effectiveness of ‘dangling DNS takeover’ attacks, a vulnerability where a forgotten DNS record points to a deleted clou…
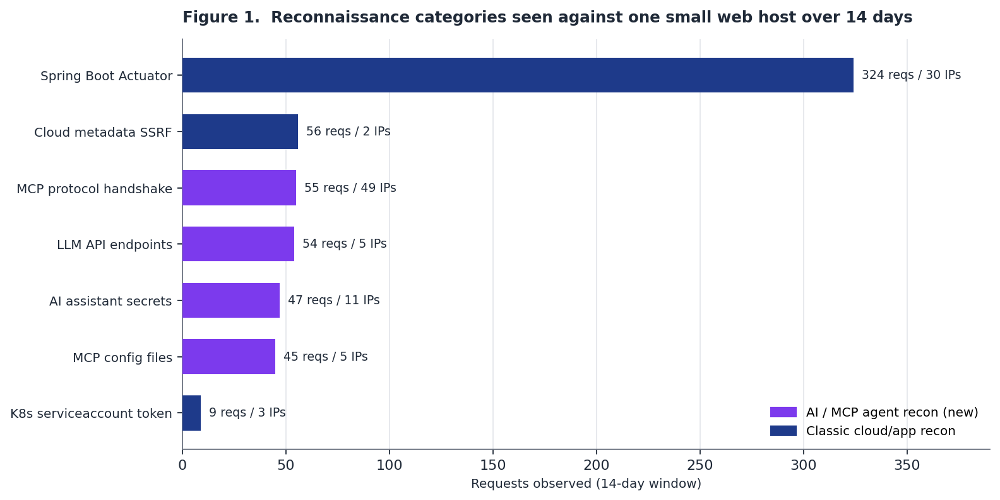
A SANS Internet Storm Center analysis reveals a widespread scanning campaign targeting servers to identify and exploit vulnerabilities related to AI assistants and local Large Language Models (LLMs). The scans are active…
A security firm, Sysdig, has identified what appears to be the first fully automated ransomware attack orchestrated by an AI agent, dubbed JADEPUFFER. The agent exploited a vulnerability in Langflow, an open-source AI ap…
A new vulnerability, dubbed 'Cordyceps,' has been discovered in CI/CD workflows, allowing unauthorized access and control over hundreds of GitHub repositories across major tech companies. The flaw stems from overly permi…
This report details a newly discovered bucket hijacking technique impacting major cloud service providers (CSPs) like Google Cloud, AWS, and Microsoft Azure. The vulnerability exploits a shared namespace design where glo…
A new supply chain attack, dubbed Hades, is leveraging the Miasma campaign to compromise 37 PyPI packages, including those used in bioinformatics and computational biology. The attack utilizes a malicious setup.pth file…
PCPJack, a threat actor initially linked to TeamPCP, has established a covert SMTP email relay network by hijacking 230 cloud servers across AWS, Google Cloud, and Azure. The operation involved converting business server…