US sanctions 10 over ATM malware scheme tied to Tren de Aragua
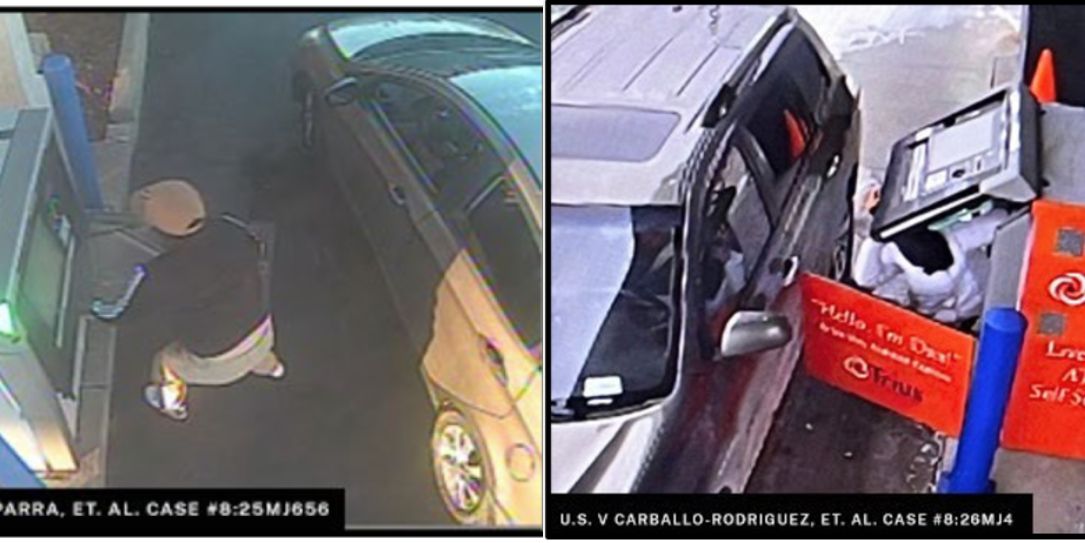
The U.S. has sanctioned 10 individuals and companies linked to a sophisticated ATM malware scheme orchestrated by Tren de Aragua, a Venezuelan criminal group.
16 article(s) in our index mention this organisation.
The U.S. has sanctioned 10 individuals and companies linked to a sophisticated ATM malware scheme orchestrated by Tren de Aragua, a Venezuelan criminal group.
The Campus Cyber Summit 2026, taking place in Lille, France, will focus on the intersection of artificial intelligence and cybersecurity. Discussions will also cover the implementation of the NIS 2 directive across Europ…
LinkedIn successfully blocked a court order that would have allowed two software companies to scrape massive amounts of user data. The companies, ProAPIs and Netswift, were accused of creating fake accounts to continuous…
The U.S. Department of Justice, in coordination with the Treasury Department's Office of Foreign Assets Control (OFAC), has disrupted the Xinbi Guarantee online marketplace, a platform facilitating scams targeting Americ…
The US is considering legislation – the ‘AI Kill Switch Act’ – requiring AI developers to maintain the ability to shut down their systems in response to growing concerns about rogue AI agents causing damage. Recent incid…
A clandestine publication alleges that a US-based automated distribution operator exposed sensitive data – including bank details, email addresses, source code, and technical access – across multiple continents via expos…
This document summarizes key vendor announcements from the 2026 Black Hat conference, focusing on advancements in cybersecurity products and services. Several companies are leveraging AI to enhance their security offerin…
DOUBLECUP, a new Russian LaaS service, is using ClickFix lures to deliver malware, specifically CountLoader (Windows and macOS) and DeviceManager (Windows and macOS). DeviceManager utilizes blockchain-based C2 resolution…
Valarian, a UK-based company focused on sovereign infrastructure control, has secured $50 million in Series A funding to bolster its platform, ACRA. ACRA is designed to provide a layer of control and governance for AI mo…
A growing trend of ‘yellow teams’ – engineering groups building both attack and defense tools – is emerging as a crucial response to the increasing threat of AI-powered cyberattacks. These teams are using advanced AI mod…
A coordinated international law enforcement operation, involving Bitdefender, Bitsight, ESET, Microsoft, and Europol, successfully disrupted the Amadey and StealC malware networks, recovering 27 million stolen credential…
This week’s ThreatDay Bulletin highlights several concerning security incidents, including browser extension abuse, macOS malware attacks, AI-powered malware delivery, and a global phishing campaign targeting travel book…
The 'Lorem Ipsum' malware campaign, initially delivered via Trojanized Microsoft Teams installers, has shifted its tactics following Microsoft's disruption of the Fox Tempest malware-signing-as-a-service provider. Now, t…
Edamame Technologies has developed a new runtime security system designed to detect and mitigate ‘code drift’ in AI coding agents. This drift, caused by agents deviating from their intended purpose, can lead to security…
Akamai has acquired LayerX, a Tel Aviv-based startup, for $205 million to bolster its Zero Trust Network Access (ZTNA) portfolio. This move reflects a growing trend among cybersecurity vendors adding secure enterprise br…
A Taiwanese student exploited vulnerabilities in the Taiwan High Speed Rail (THSR)'s TETRA radio system, causing a 48-minute delay in service by spoofing an emergency alarm. This incident highlights broader cybersecurity…