vulnerability
Multiples vulnérabilités dans les produits SonicWall (04 novembre 2026)
SonicWall has announced multiple vulnerabilities in its GMS products, primarily impacting versions 9.5.2 and earlier.
HighCVSS 9.1
Covered by 4 sources: CERT-FR, The Hacker News, SecurityWeek, SANS Internet Storm Center.
SonicWall has announced multiple vulnerabilities in its GMS products, primarily impacting versions 9.5.2 and earlier.
SonicWall has warned of two unpatched vulnerabilities in its end-of-life Global Management System (GMS) that are actively being exploited. SonicWall is urging users to upgrade to SonicWall Network Security Manager to mit…
A vulnerability in OpenSSH versions prior to 10.6p2 allows an attacker to bypass security policies.
Cisco and WatchGuard have released patches for several vulnerabilities in their products, including RCE and authentication flaws. The Node2Shell vulnerability stems from a zero-day flaw in Google's Brotli compression lib…
A high-severity vulnerability, dubbed ‘SSHole,’ in OpenSSH allows attackers to bypass password authentication and gain root access on vulnerable systems. Patches are available, and immediate mitigation is advised by disa…
SonicWall has released a patch to address a critical vulnerability (CVE-2026-19868) in its SonicOS operating system that could allow attackers to bypass SAML authentication and potentially bypass multi-factor authenticat…
CISA has added a high-severity vulnerability (CVE-2026-19868) to its KEV catalog in SonicWall SonicOS, allowing attackers to bypass SAML authentication and MFA.
Hackers are actively exploiting a recently patched authentication bypass vulnerability (CVE-2026-123158) in OpenSSH, allowing them to gain unauthorized access to accounts, including root, by supplying specific password l…
CISA has added four vulnerabilities – IBM Aspera Faspex, SignalWire FreeSwitch, OpenBSD OpenSSH, and GPUStack – to its list of actively exploited flaws. Federal Civilian Executive Branch agencies are urged to apply patch…
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning about active exploitation of vulnerabilities in IBM Aspera Faspex and SignalWire FreeSwitch.
A vulnerability has been discovered in Sonicwall SonicOS that could lead to data integrity and confidentiality issues.
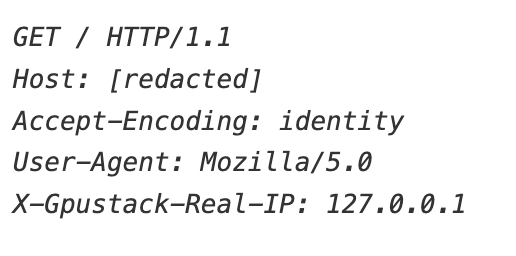
A trivial authentication bypass vulnerability (CVE-2026-102895) in GPUStack has been actively exploited. GPUStack, used for managing GPU clusters in AI workloads, is vulnerable in all versions prior to 2.2.0.