

threat-intel
Using Microsoft Graph and Powershell - Risk Detection Commands, (Thu, Aug 20th)
Medium
Summary
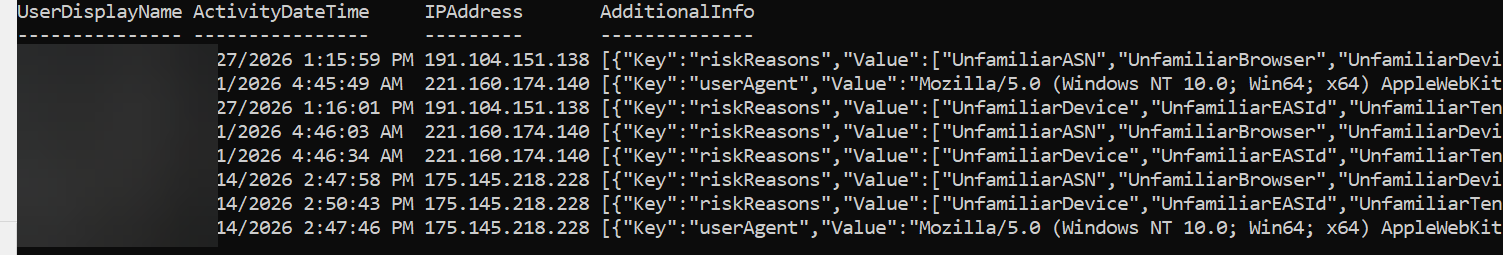
This article details how to use Microsoft Graph PowerShell commands to identify risky login attempts. By leveraging the `Get-MgRiskDetection` command, security analysts can detect logins originating from unusual locations (based on IP address, subnet, ASN, or location) or using unfamiliar devices. The process involves extracting risk reasons (like ‘UnfamiliarDevice’, ‘UnfamiliarEASId’, ‘UnfamiliarTenantIPsubnet’) and associating them with user activity, enabling proactive threat detection and investigation.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data