

The Behavior of Coordinated SSH Brute Force Attacks over the last three months [Guest Diary], (Wed, Jun 17th)
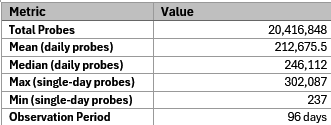
This report details a three-month analysis of coordinated SSH brute-force attacks conducted using a honeypot system, highlighting a correlation between attack activity and geopolitical events, law enforcement actions, and cybersecurity advisories. The analysis, conducted by SANS.edu, revealed a significant surge in attacks coinciding with tensions between Iran, Israel, and the United States, alongside opportunistic attacks following CISA advisories. The findings indicate a complex landscape of automated botnets and advanced persistent threats, with specific IP addresses exhibiting coordinated scanning behavior across multiple countries.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data