

threat-intel
More RMM Tools In the Wild, (Tue, Oct 6th)
Info
Summary
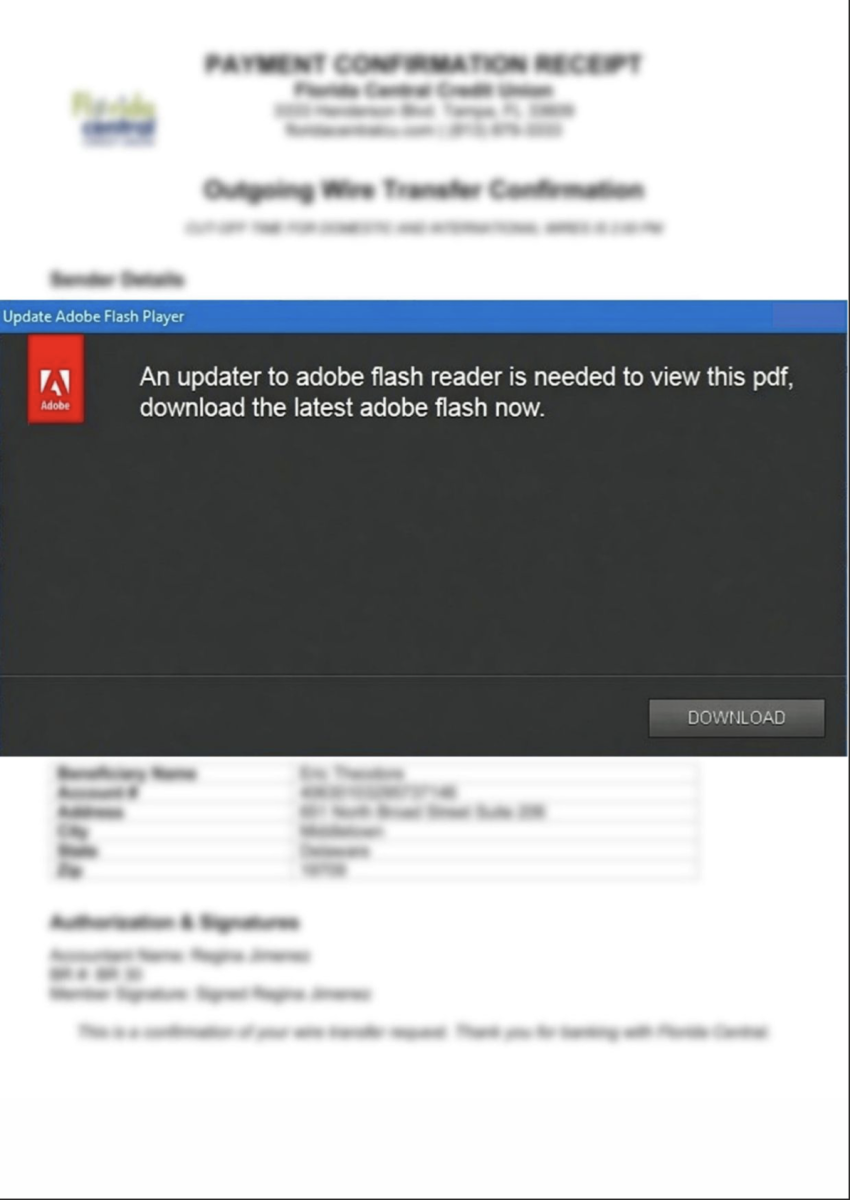
Threat actors are abusing the Action1 RMM tool to deliver malicious payloads. The attack begins with a phishing email containing a fake PDF invoice that redirects to a VBS file. This VBS file then downloads and installs an MSI archive containing files associated with the Action1 RMM tool, which installs itself as a service for persistence. The files are signed with an Action1 Corporation certificate. The threat actors are leveraging Action1's cloud infrastructure.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data