

Guildma (Astaroth) malware infection from Brazilian Portuguese email, (Tue, Sep 1st)
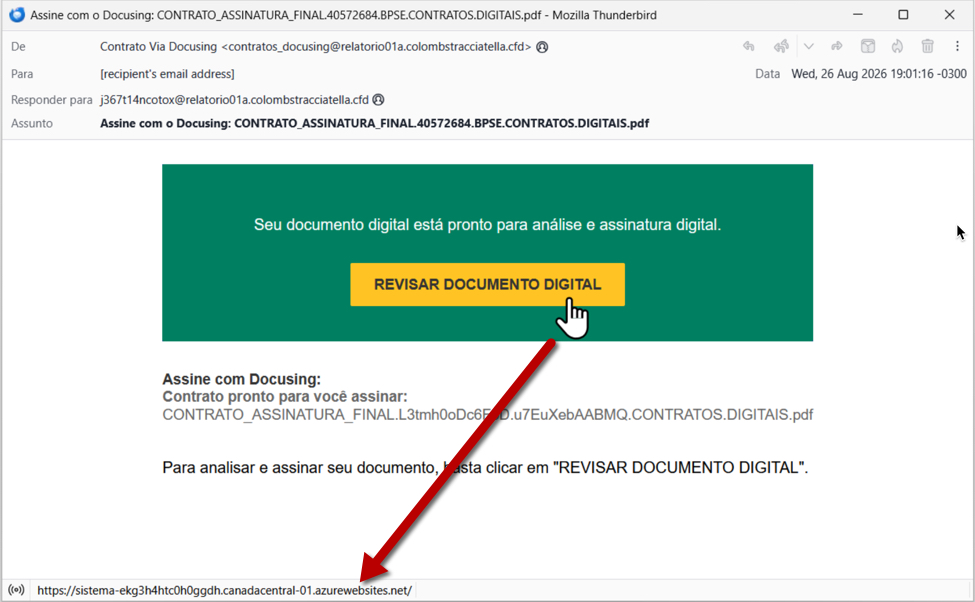
A Guildma (Astaroth) malware infection was delivered via a Brazilian Portuguese email link, targeting Windows hosts. The initial attack involved a geofenced link, requiring a Brazilian IP address and Portuguese language settings. The attacker used a zip archive containing a Windows shortcut to deliver a persistent AutoIt script, leveraging alternate data streams to install the malware. Indicators of compromise included specific SHA-256 hashes and communication with several domains, including those linked to a GitHub campaign. The campaign is ongoing and utilizes legitimate domains like WhatsApp and GitHub for persistence.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data