

malware
An Example of Stack String in High Level Language, (Sat, May 23rd)
Medium
Summary
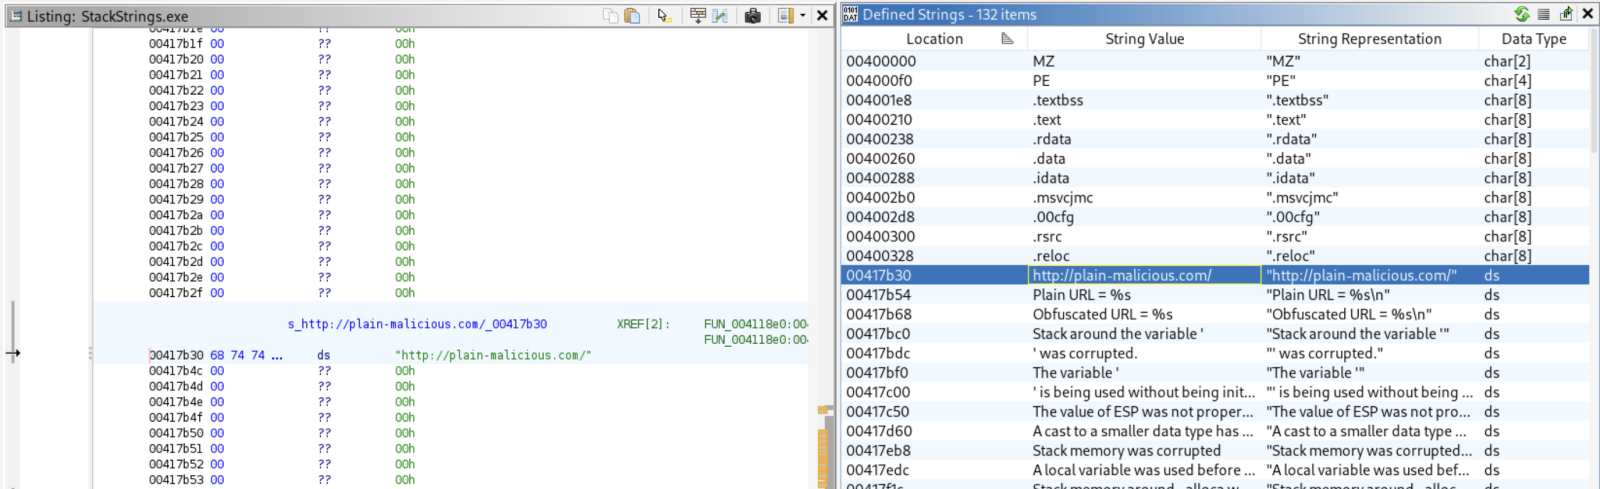
This article discusses a malware obfuscation technique called "stack strings," where strings are dynamically constructed on the stack at runtime rather than being stored as contiguous data in the binary. The example demonstrates how this technique can evade simple detection tools like "strings" and "pestr" by utilizing hexadecimal encoded characters. The article highlights the use of assembly code and provides a C code example illustrating the technique, along with a demonstration of how to identify the string using a shell and tools like Floss.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data