

malware
LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th)
High
Summary
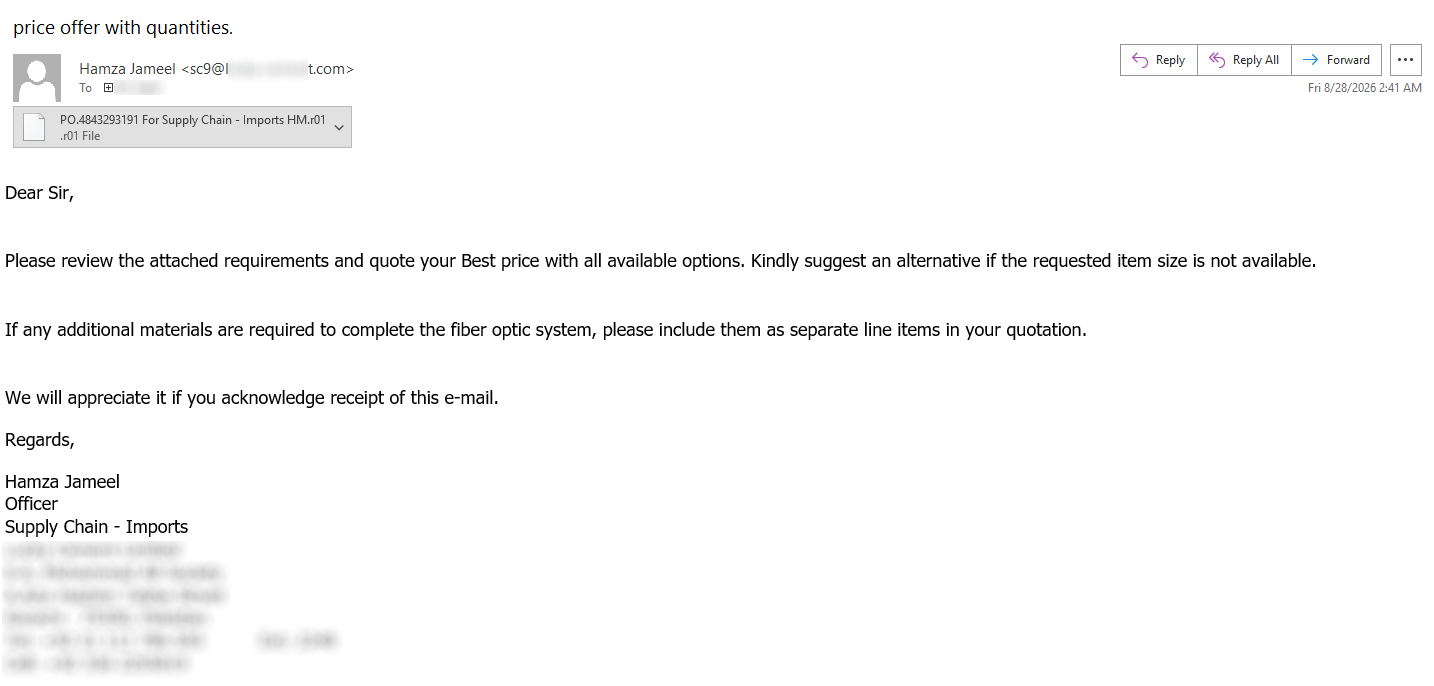
A malspam campaign delivered a malicious attachment containing a LausivLoader script. The script, after removing comments, obfuscated code, and attempts to register a scheduled task, ultimately downloaded and executed a second .NET executable. This executable, in turn, downloaded a PNG image containing a hidden payload, leveraging an 'iTXt' chunk to conceal the malicious code. The entire process involved multiple stages, including data exchange via environment variables and attempts to evade security measures like AMSI.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data