

threat-intel
CVE-2024-40766: The Patch Fixed the Bug. Nobody Fixed the Configuration., (Tue, Jun 23rd)
Critical
Summary
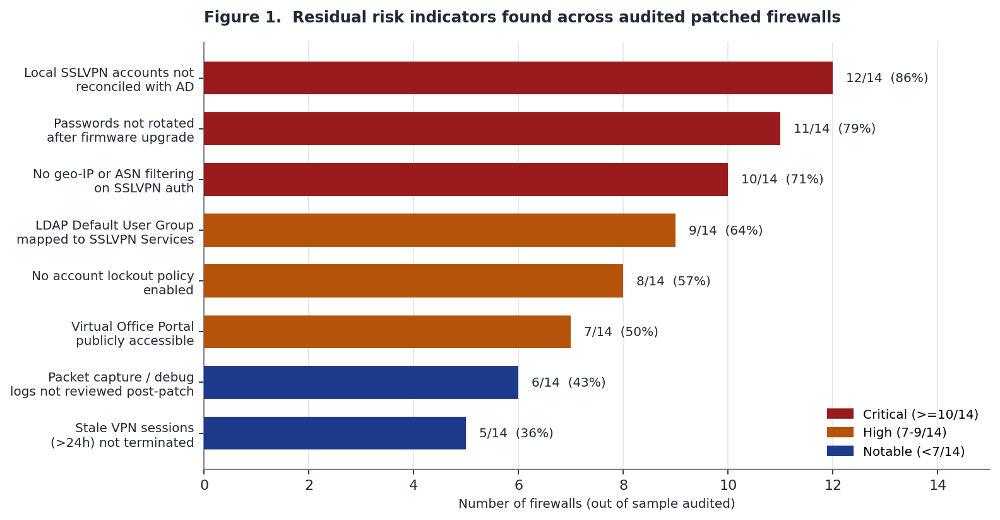
This report details a significant ongoing cyber threat targeting SonicWall firewalls exploiting CVE-2024-40766, a critical access control vulnerability. Ransomware groups, notably Akira and Fog, have been actively leveraging this flaw since September 2024, primarily targeting businesses using SSLVPN for remote access. The issue is exacerbated by misconfigurations, such as unreset local passwords after firmware upgrades, and the continued operation of vulnerable Gen 6 devices, leading to widespread compromise and data breaches.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data