

threat-intel
Even MOAR Powershell, looking at Entra logins - the good, the bad and the password sprays, (Fri, Aug 21st)
Medium
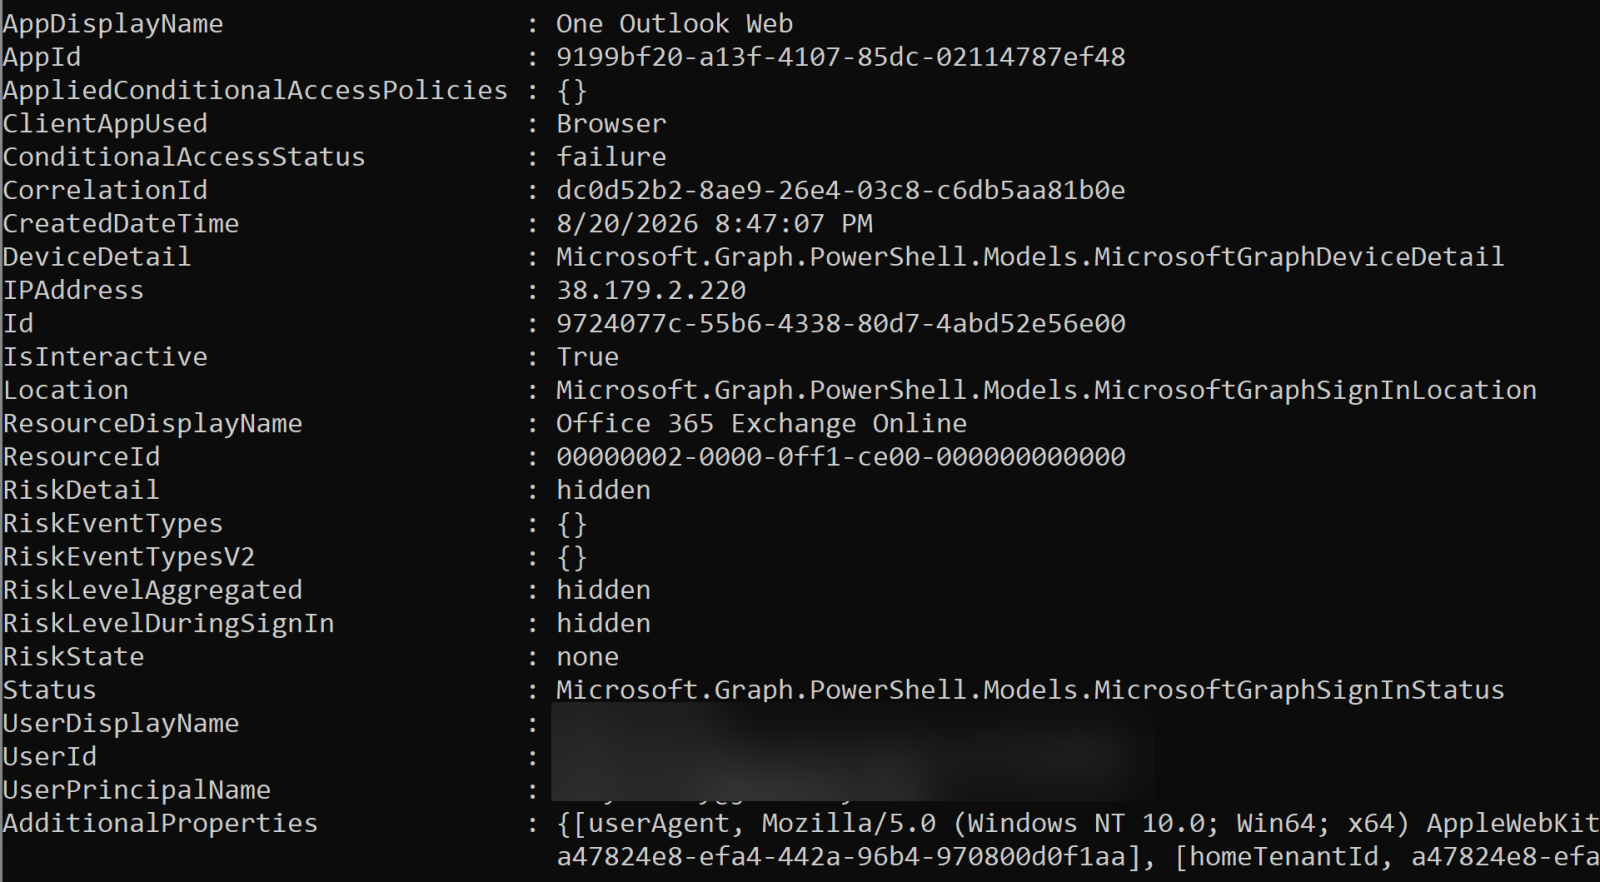
Summary
This article details a method for identifying password spray attacks and unusual login activity within Microsoft Entra (formerly Azure Active Directory) logs. By analyzing login events and filtering for unexpected countries and failed logins, security analysts can proactively detect and mitigate password spraying attacks, ultimately strengthening Entra security posture. The author successfully used this technique to help a client improve their conditional access policies.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data