

malware
DOUBLECUP's PNG Payload, (Mon, Aug 24th)
Medium
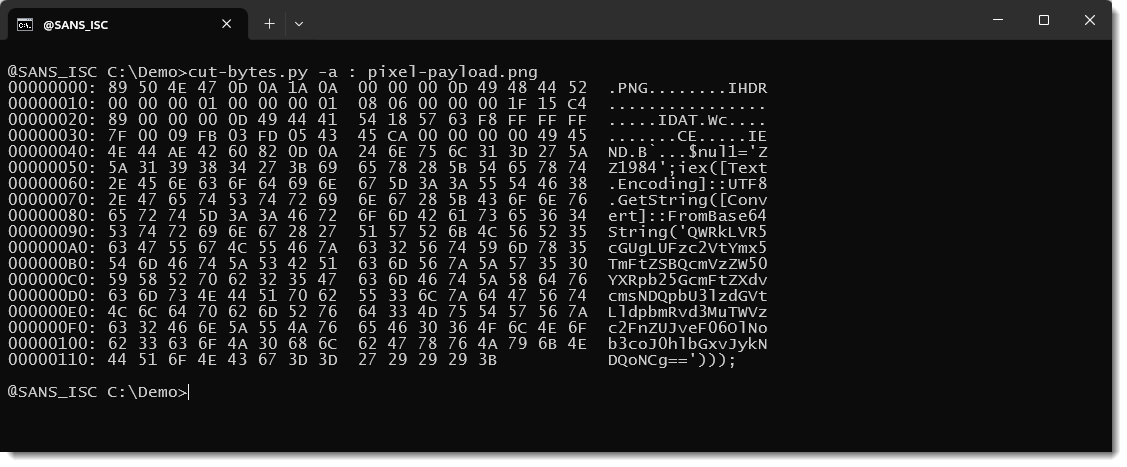
Summary
A new DOUBLECUP malware campaign utilizes a clever technique to bypass traditional steganography detection. The malware, delivered via PNG images, uses a simple PowerShell script appended to the file, easily extracted using the Windows `FINDSTR` command, avoiding the need for specialized extraction tools.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data