

threat-intel
CISA Admin Leaked AWS GovCloud Keys on Github
High
Summary
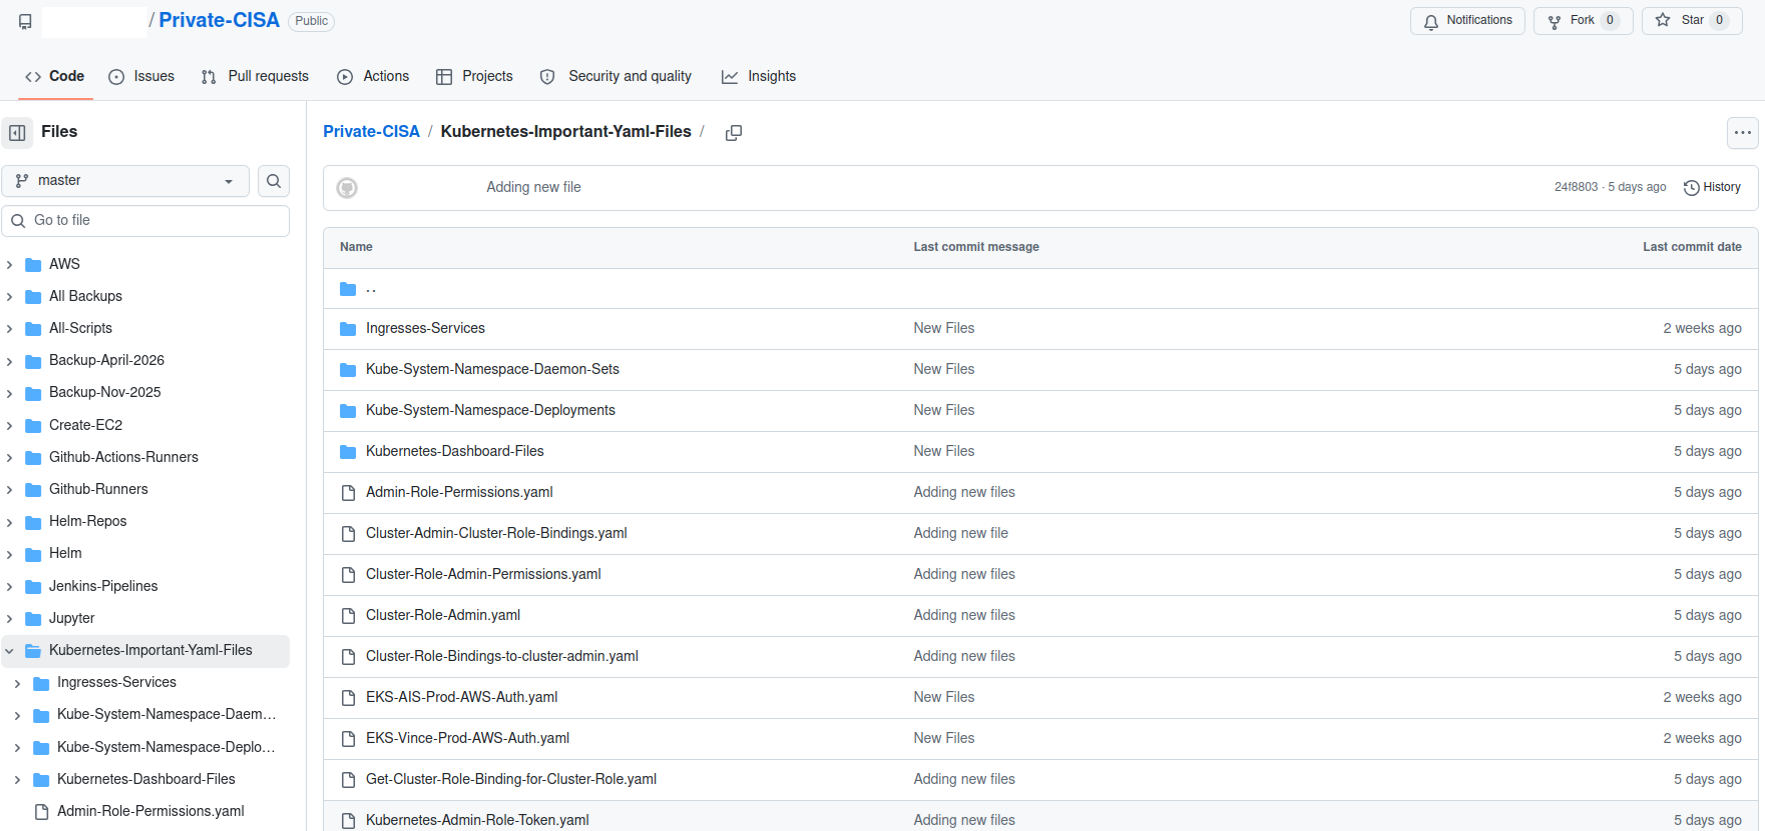
A contractor for CISA inadvertently exposed highly privileged AWS GovCloud credentials and internal CISA system information via a public GitHub repository. The repository contained plaintext passwords, cloud keys, and logs, representing a significant security lapse and a potential risk to sensitive government data. While CISA stated there was no indication of data compromise, the incident highlights vulnerabilities in developer practices and the importance of secure code repository management.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data