

Honeypot-Omaha and batch.py [Guest Diary], (Wed, Sep 2nd)
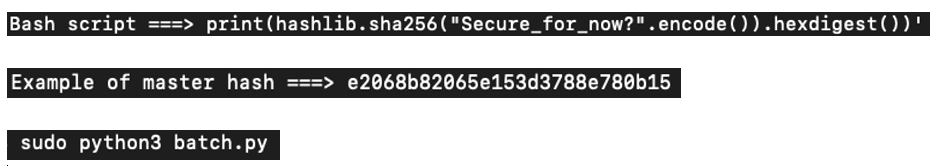
This guest diary details the creation and use of ‘batch.py’, a Python script designed to analyze logs and data related to honeypot-Omaha, a decoy system set up by the Internet Storm Center. The script automates the process of gathering intelligence from various log sources (cowrie, zeek, etc.) and presenting it in a structured format, allowing analysts to quickly identify threat actors, their methods, and potential vulnerabilities. The script is built around a pipeline of phases, each designed to extract and correlate specific types of data, from usernames and passwords to exploited vulnerabilities and command-and-control activity. It emphasizes a ‘long tail’ analysis approach, focusing on persistent activity and attempts to cover tracks.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data