

threat-intel
TerminalFix: PNG Steganography, (Mon, Sep 21st)
High
Summary
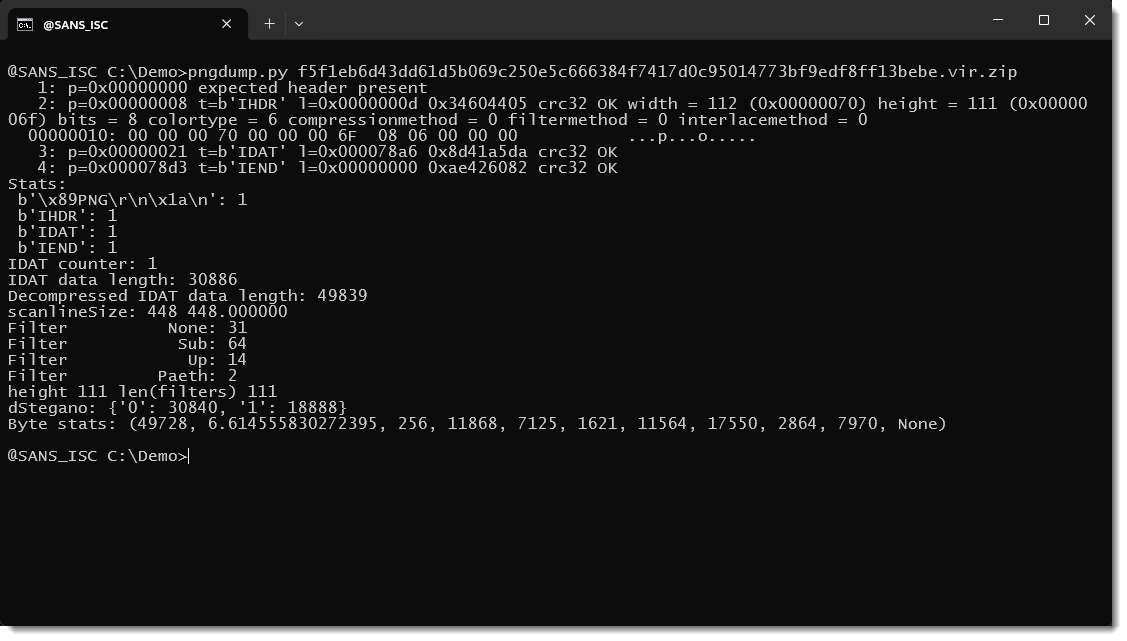
A threat actor campaign, led by Didier Stevens, is utilizing PNG files employing steganography to conceal malicious payloads. The campaign uses a reverse tunnel and a multi-stage intrusion, with the PNG files containing a DLL payload hidden within the image data. The threat actors are utilizing all available bits of the PNG image to embed the payload, making it difficult to detect visually.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data