

Recent DShield SIEM Update, (Tue, Jul 14th)
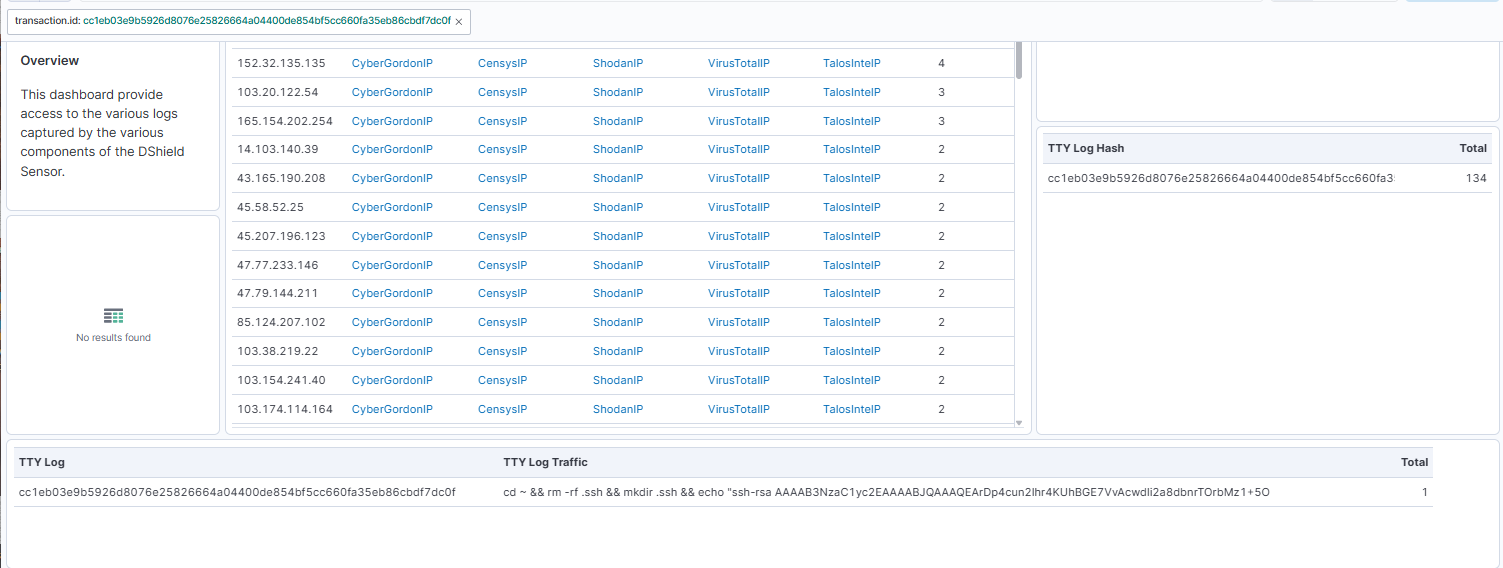
The DShield SIEM, a honeypot monitoring system, received a recent update incorporating new features and improved logging capabilities. Specifically, the system now collects TTY logs and integrates Suricata alerts, providing enhanced insights into attacker activity. These additions are designed to improve threat detection and analysis within the DShield environment. The update includes a GitHub repository for configuration and a planned workshop at SANSFIRE 2026.
The DShield SIEM, a honeypot monitoring system maintained by ISC.org, recently received an update to its SIEM infrastructure. This update focuses on bolstering the system's ability to capture and analyze attacker behavior. The core addition involves the integration of TTY logs, which are now collected and parsed daily at 23:58Z. These logs are base64 encoded before transmission to the SIEM and decoded within Kibana for review. The logs provide a transcript of activity reviewed in Kibana, linked to transaction IDs and event hashes.
Furthermore, Suricata alerts have been added to the DShield dashboards, linking to all other logs for a more comprehensive view of potential attacks. The dashboard now allows for the replication of queries selected in one sub-dashboard to other sub-dashboards, streamlining analysis. A Threat Map is also available to visualize traffic movement and log activity.
Jesse and the author are hosting a workshop at SANSFIRE 2026, encouraging attendees to join the Honeypot Workshop in Independence A - West (Level 5B) at 6:45 PM. The update includes a GitHub repository ([https://github.com/bruneaug/DShield-SIEM/tree/main](https://github.com/bruneaug/DShield-SIEM/tree/main)) for configuration and a separate repository ([https://github.com/bruneaug/DShield-SIEM/blob/main/AddOn/Configure_Suricata.md](https://github.com/bruneaug/DShield-SIEM/blob/main/AddOn/Configure_Suricata.md)) for Suricata integration. The TTY logs are parsed once per day and uploaded directly into DShield SIEM with filebeat.