

Iranian cyber spies used fake MRI scan results to hack ‘enemy of regime’
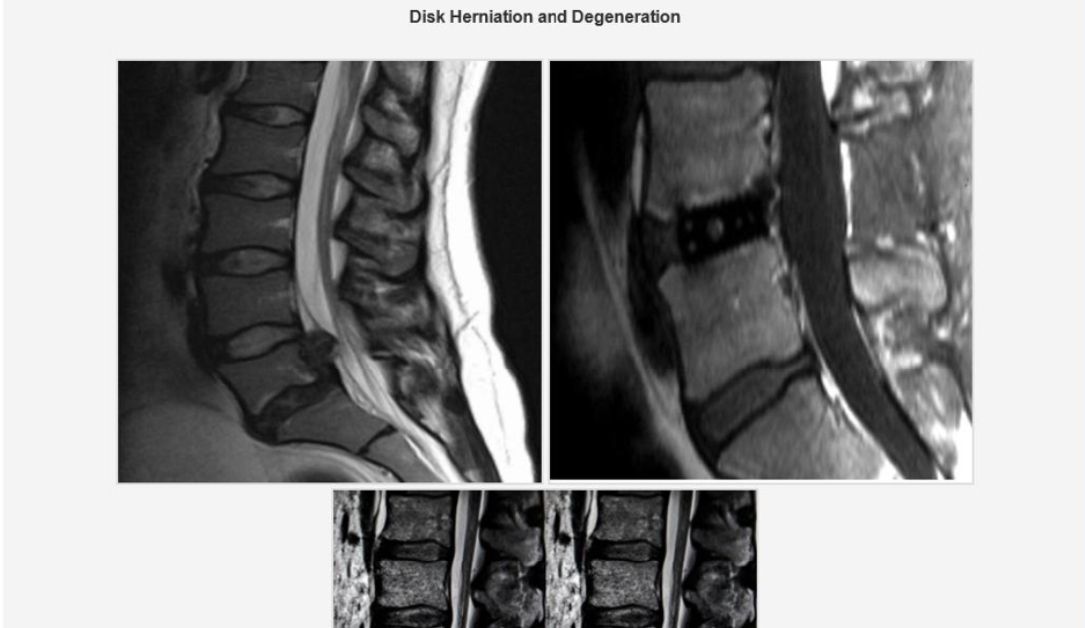
British, American, and Dutch intelligence agencies have issued a warning about a spyware tool, dubbed CHOSEN BRICK, being used by Iranian state-sponsored hackers to target individuals perceived as threats to the Iranian regime. The malware is delivered through sophisticated social engineering tactics, including fake MRI scan results, and is used to gather extensive personal data, potentially leading to real-world physical attacks and kidnappings. The agencies urge organizations to share the warning and help employees check their devices.
British, American, and Dutch intelligence agencies have issued a joint warning about a sophisticated spyware tool, CHOSEN BRICK, being utilized by Iranian state-sponsored hackers to target individuals deemed a threat to the Iranian regime. The campaign has been ongoing since at least 2025 and involves extensive social engineering to build trust with victims.
CHOSEN BRICK is delivered through a range of lures, most notably a fake MRI scan depicting a disk herniation, designed to gain the victim’s confidence. The malware is primarily used to harvest a wide range of data from targeted devices, including contacts, email inboxes, and social media messages, as well as capturing screen content and microphone access. This data is then used to create a ‘pattern of life’ – a detailed map of the victim’s location, contacts, and daily routine – increasing the physical risk to those targeted.
The agencies warn that personal details stolen this way have surfaced on pro-Iranian leak sites, further harassing the victims. The campaign is characterized by a highly personalized approach, with operators tailoring their tactics to each individual target, often initiating contact via messaging platforms like WhatsApp and Telegram, impersonating known contacts or technical support.
Malware files are disguised to match the pretext, including mimicking legitimate products such as Pictory, RunwayML, Norton Antivirus, Telegram, Adobe Flash Player, and KeePass. The CHOSEN BRICK malware itself is designed exclusively for Windows systems and is engineered to survive device reboots by relaunching at login. It also employs techniques to evade detection by Microsoft Defender by adding exclusions.
Once installed, the malware utilizes Telegram for command and control, with each victim assigned a separate Telegram bot to limit the risk of one compromised device exposing others. Stolen files are also transmitted through Telegram alongside other commercial cloud-storage services, utilizing proxies to conceal traffic. The NCSC has observed the use of similar Telegram-based malware targeting Iranian dissidents and journalists since fall 2023, linked to “Handala Hack,” an online persona operated by MOIS and connected to another group, “Homeland Justice.”
In March, the U.S. State Department reissued a $10 million reward for information on hackers connected to Iranian cyber actors following a compromise of FBI Director Kash Patel’s personal email account. The FBI also seized numerous leak sites tied to the MOIS used to host stolen information. The threat posed by Iranian surveillance extends beyond cybersecurity, with British security services tracking over 20 potentially lethal Iran-backed plots in the past year, including threats against journalists and opponents of the Iranian government.