

malware
Evil MSI Background: BASE64 Statistical Analysis, (Mon, Jun 15th)
Medium
Summary
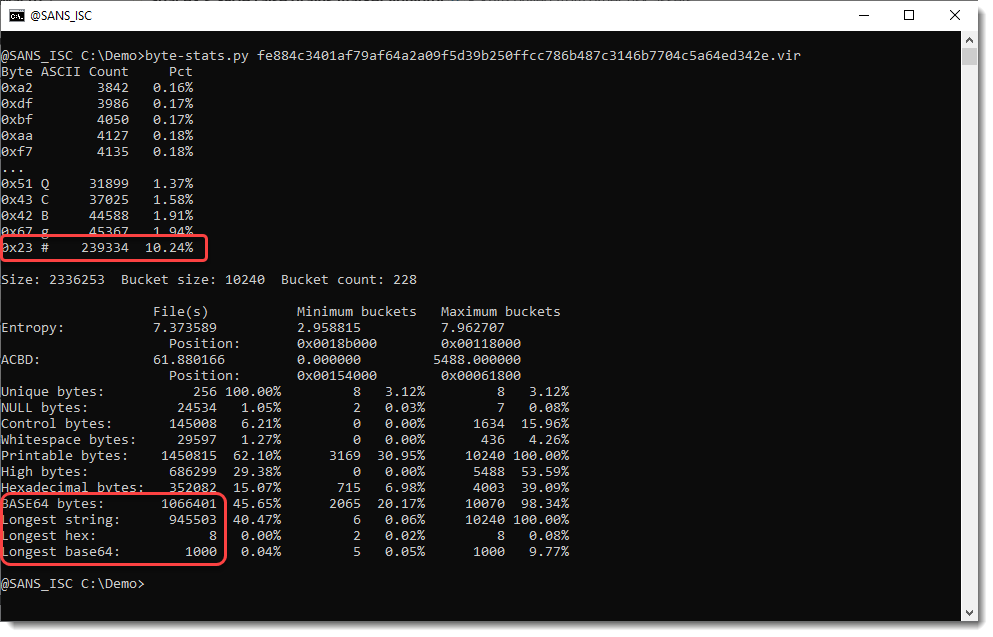
This report details the analysis of the "Evil MSI Background" file, a suspicious JPEG containing a hidden payload. The analysis, conducted by Didier Stevens, utilized tools like `byte-stats.py` and `base64dump.py` to uncover a custom BASE64 encoding scheme, ultimately revealing a reversed PE executable. The investigation highlights the importance of statistical analysis and reverse engineering techniques when dealing with obfuscated malware.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data