

malware
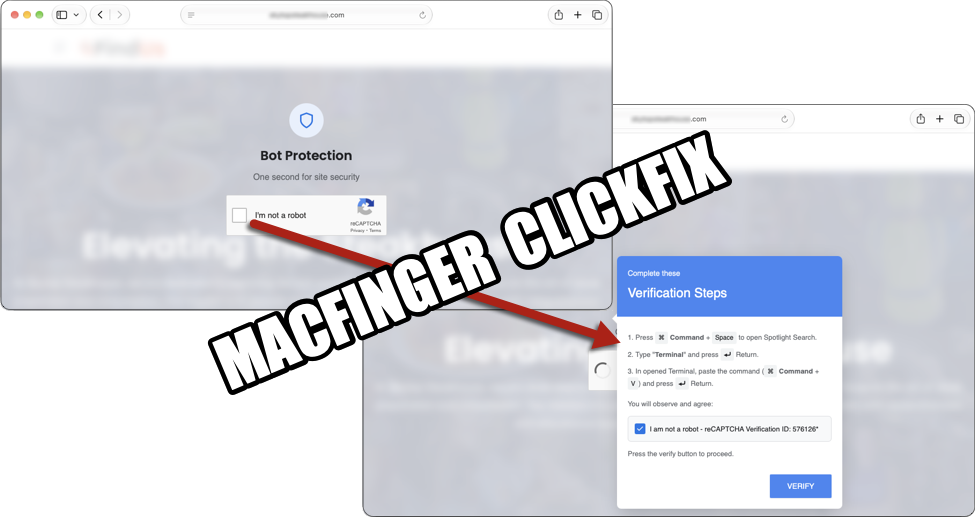
A Closer Look at Malware From the Macfinger ClickFix Campaign, (Fri, Sep 25th)
Medium
Summary
This report details an ongoing campaign, Macfinger ClickFix, utilizing a novel malware loader and information stealer targeting macOS hosts. The campaign utilizes a series of domain names and URLs to host and deliver the malicious payload. The malware is designed to gain access to various applications and folders, including Terminal.app, to facilitate data exfiltration.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data