

ransomware
From a VHDX File to a Remcos RAT, (Tue, Jun 16th)
High
Summary
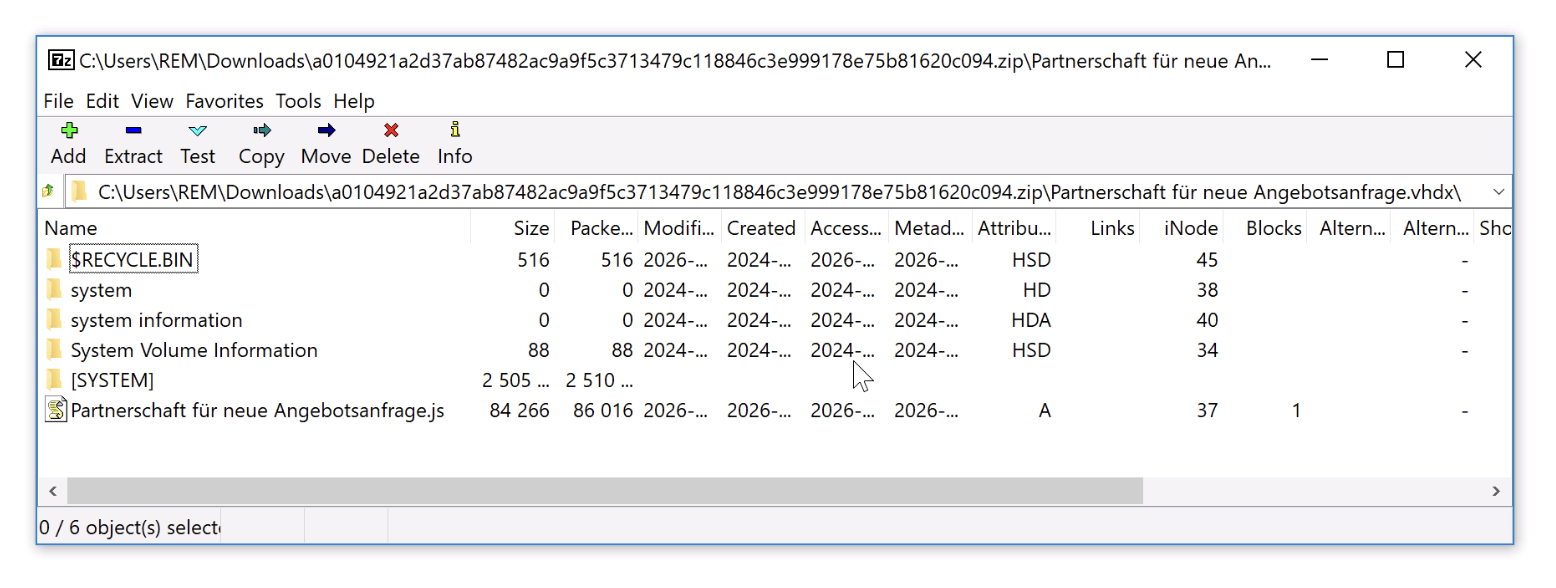
A malicious ZIP archive, containing a VHDX file, was discovered utilizing a multi-stage attack chain to deploy the Remcos RAT. The initial delivery involves a JavaScript payload that leverages WMI and PowerShell to execute a reconstructed PowerShell script, ultimately downloading and executing the Remcos RAT. This technique bypasses traditional security controls by obfuscating the initial stages and utilizing less-monitored methods like WMI and PowerShell.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data