

‘CanisterWorm’ Springs Wiper Attack Targeting Iran
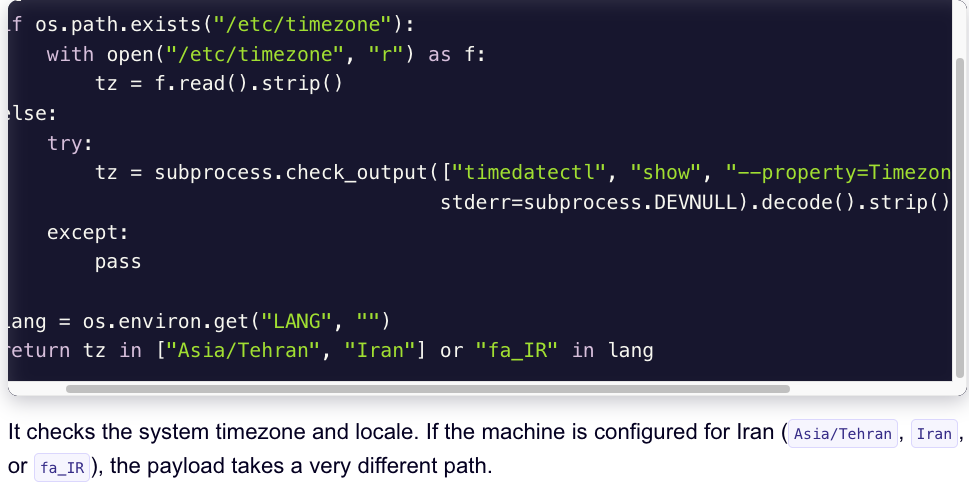
A financially motivated cybercrime group, TeamPCP, is deploying a wiper attack targeting Iran, leveraging a self-propagating worm that exploits vulnerabilities in cloud services like Azure and AWS. The group gained initial access through a supply chain attack against Trivy, a vulnerability scanner from Aqua Security, and is now using ICP canisters to distribute the wiper payload, targeting systems based on timezone and locale. This attack highlights the group's industrialization of existing vulnerabilities and their use of automation to create a cloud-native exploitation platform.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data