

The Evil MSI Background is Back!, (Fri, Jun 5th)
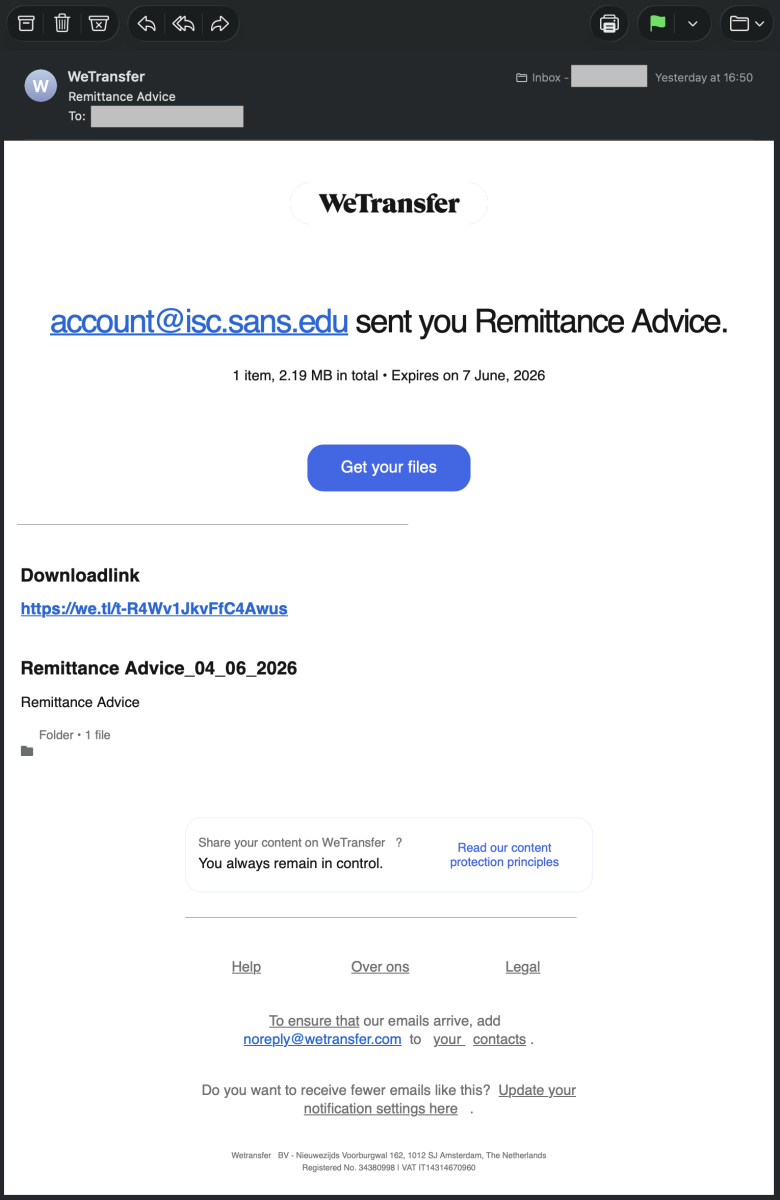
This report details a recent cyberattack utilizing a classic MSI-branded JPEG payload, a technique previously documented by the SANS Internet Storm Center. The attack began with a phishing email containing a WeTransfer link, leading to a JavaScript file that executed PowerShell commands to download and execute a malicious .NET DLL. The attacker leveraged Cloudflare workers and R2 storage services to host the payloads, employing obfuscation techniques like ROT13 and Base64 encoding to evade detection. The attack utilizes a modified TaskScheduler library and a PNG image potentially containing a further payload.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data