

threat-intel
Linux Process Name Masquerading, (Wed, Jun 24th)
Medium
Summary
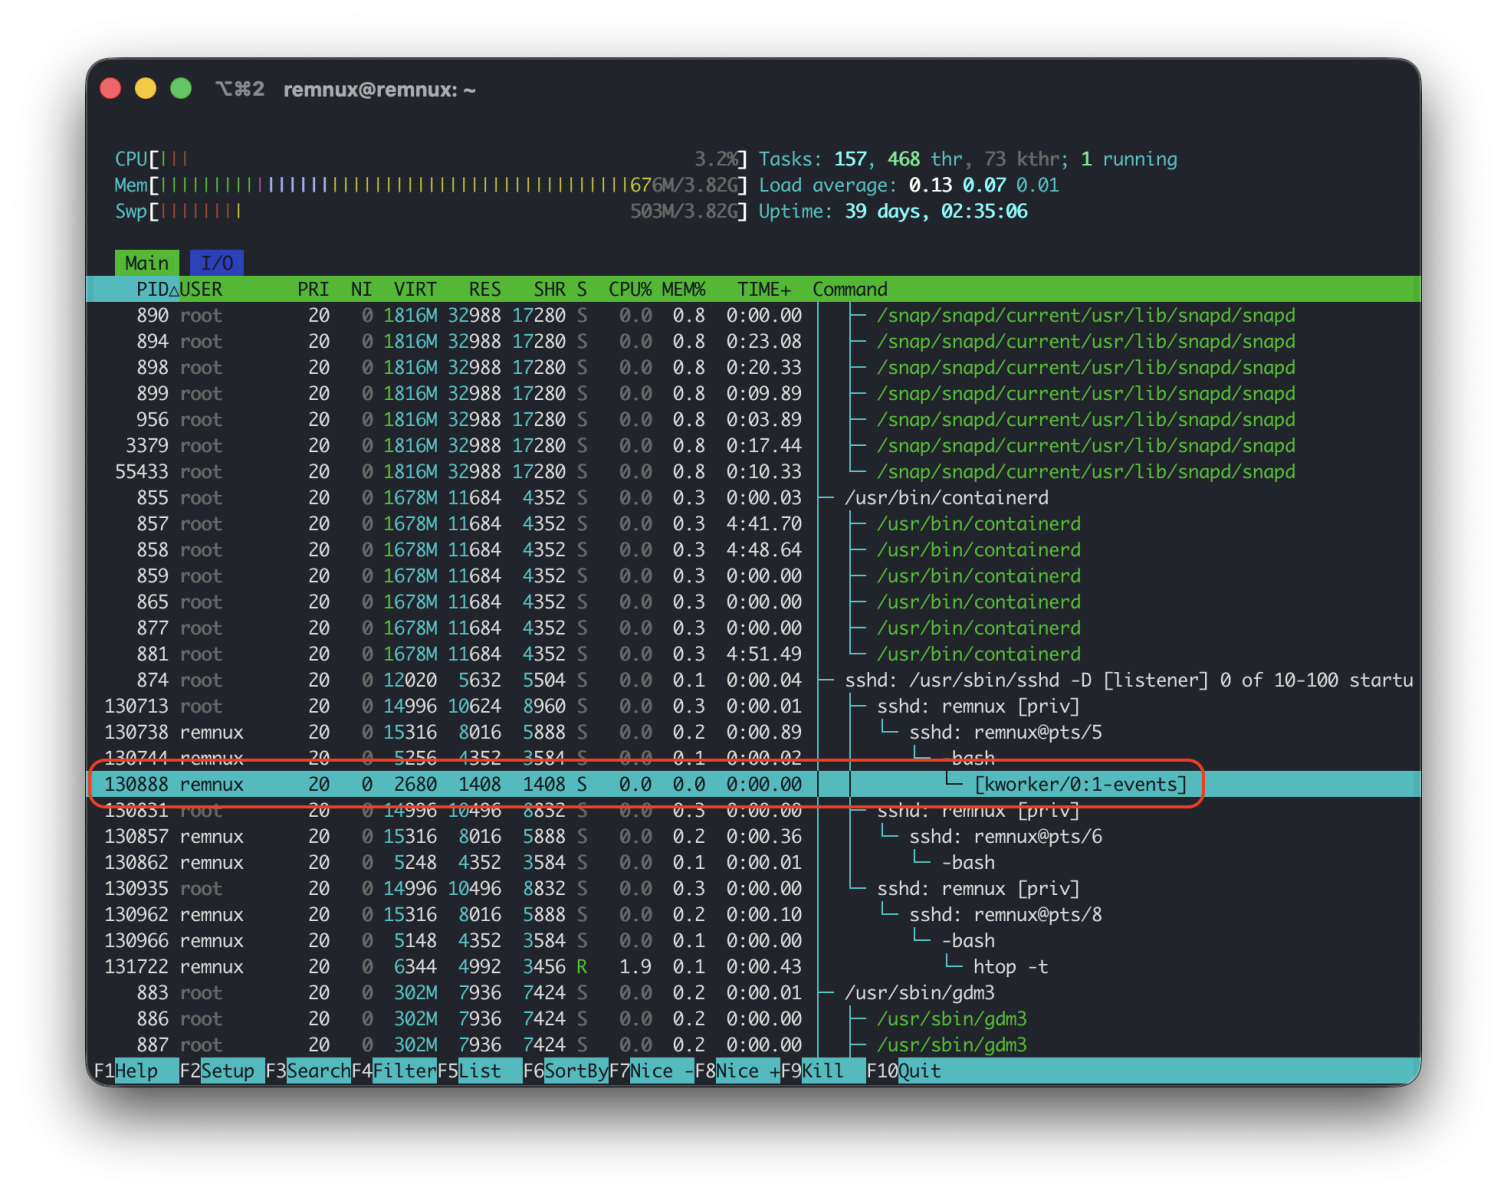
This SANS Internet Storm Center diary details a technique used by attackers, specifically the Velvet Ant Chinese group, to mask process names in Linux systems. Attackers modify the ‘comm’ and ‘cmdline’ entries in the /proc/<pid> directory to hide the true name of a malicious process, making it less likely to be detected by security tools. The article provides a proof-of-concept (PoC) C program demonstrating how to achieve this by manipulating the prctl() system call and highlights the use of tools like Kunai to detect this obfuscation technique.
Summary written automatically in our own words from the original article, which belongs to its publisher and remains the reference. It may contain errors. Sources & data