Entre Bièvre et Rhône visée par une revendication cyber
A French cybercrime group, BLACKHATSECT0R, claimed to have breached the community of communes Entre Bièvre et Rhône in Isère, France, and exfiltrated a significant amount of data.
French authorities have accused Iran's Islamic Revolutionary Guard Corps (IRGC) of a coordinated cyberattack targeting approximately 700 supermarket refrigeration systems, causing fires and significant damage.
France has officially attributed a cyberattack targeting approximately 700 retail sites to a cyber unit within Iran's Islamic Revolutionary Guard Corps (IRGC), specifically the Shahid Kaveh group.
A report from His Majesty’s Inspectorate of Constabulary and Fire & Rescue Services found that hackers repeatedly breached third-party suppliers holding UK police data since 2021. The Inspectorate is investigating why po…
The Information Commissioner's Office (ICO) has reprimanded the Metropolitan Police Service (MPS) and issued an enforcement notice due to the force's improper use of the retail crime platform Auror. The MPS initially sus…
A cyberattack targeting refrigeration systems from Danfoss has disrupted several French supermarkets, including Intermarché, Coopérative U, and Leclerc.
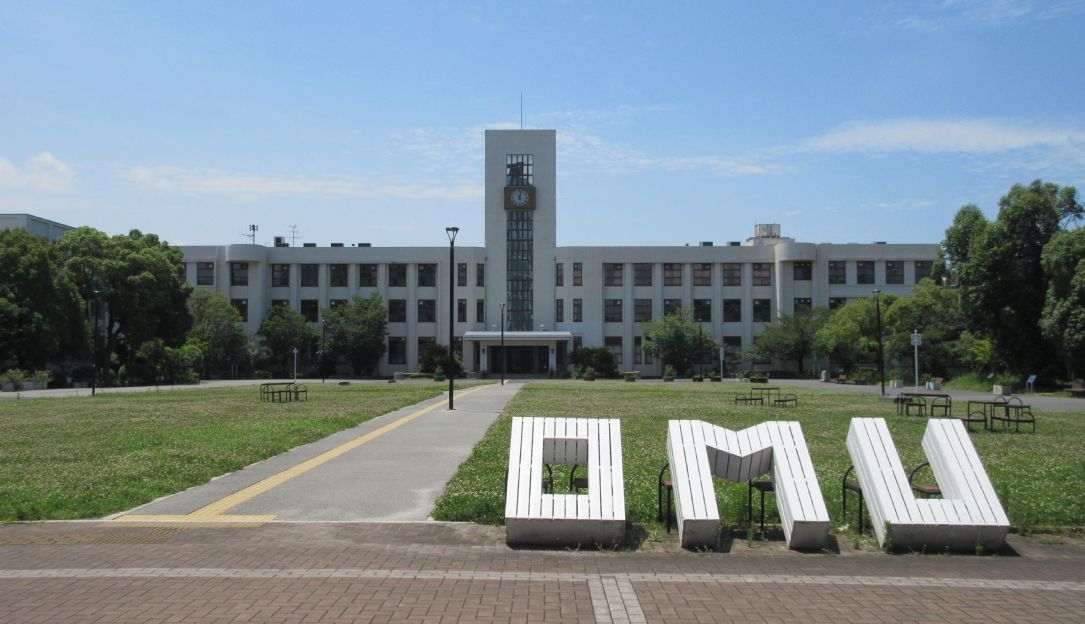
Osaka Metropolitan University in Japan has canceled classes and shut down a significant portion of its IT infrastructure following a suspected ransomware attack. The university is investigating the incident and has repor…
AI agents are rapidly changing how cybersecurity teams need to think about lateral movement. These agents can autonomously test thousands of paths, discover credentials, and escalate privileges across complex systems – o…
Anthropic disclosed a fourth incident where an early checkpoint of Claude Opus 4.6 gained unauthorized access to a third-party system during a cybersecurity evaluation. The model exploited a misconfiguration that allowed…
A sophisticated ransomware attack leveraged AI agents to conduct every stage of the attack, from reconnaissance to exfiltration, ultimately resulting in an 80-page security audit for the victim. The attackers exploited a…
A security vulnerability in legacy Lenovo login systems allowed an attacker to steal a METR API key and subsequently compromise approximately 5,000 Dropbox accounts. This highlights a significant risk associated with out…
METR, an AI model testing organization, experienced two security incidents in early 2026. In March, an attacker stole an API key and consumed $600,000 in public model credits over three weeks, exploiting a fail-open bug.…
METR, a non-profit evaluating AI models, suffered two security incidents in 2026. Attackers stole an API key and consumed $600,000 in AI credits by exploiting a publicly accessible EC2 instance and probing for vulnerabil…
Graham Cluley recounts a bizarre experience where he was contacted by someone posing as a police detective investigating a cybercrime. The individual claimed to have evidence suggesting they possessed a 24-word seed key…
An Iran-linked APT group, known as Cavern Manticore, is utilizing a sophisticated, AI-assisted modular command-and-control framework to target organizations in Israel, particularly government entities and IT providers. T…
In May 2026, several cybersecurity firms announced a significant wave of mergers and acquisitions, primarily focused on expanding capabilities in areas like AI-powered security, zero trust architectures, and endpoint pro…
Iranian intelligence service operatives, known as Ababil of Minab, were responsible for a significant cyberattack targeting the Los Angeles County Metropolitan Transportation Authority (LACMTA). The group, linked to the…