Scans for LiteLLM/Starlette (CVE-2026-42271, CVE-2026-48710), (Mon, Nov 16th)
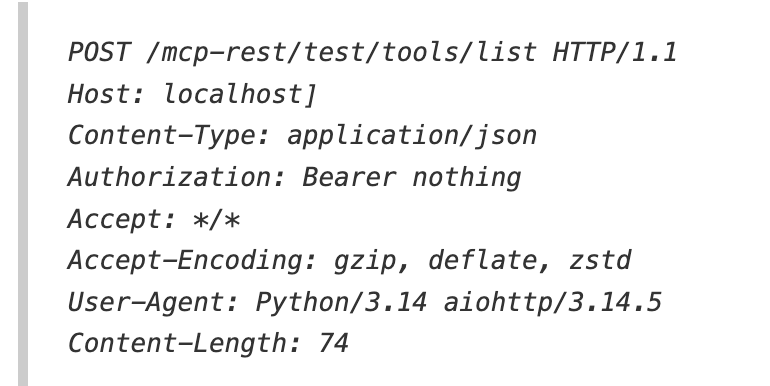
Researchers at SANS Internet Storm Center detected requests targeting a LiteLLM endpoint, attempting to exploit CVE-2026-42271 and CVE-2026-48710 in Starlette.
A critical vulnerability (CVE-2026-61500) in Rejetto HTTP File Server (HFS) has been exploited by hackers, allowing them to bypass authentication and achieve remote code execution. Initial exploitation attempts have been…
A critical vulnerability (CVE-2026-61500) in Rejetto HTTP File Server is being actively exploited, allowing attackers to gain administrative access and execute code. A patch was released in July 2026.
A critical SQL injection vulnerability (CVE-2026-9586) in Sangoma Switchvox is being actively exploited in the wild, allowing attackers to execute arbitrary code and access sensitive data. The US Cybersecurity and Infras…
The article highlights a growing concern among CISOs that traditional vulnerability management – relying on a massive influx of CVEs and subjective CVSS scores – is no longer sufficient to meet the demands of modern boar…
This document summarizes key vendor announcements from the 2026 Black Hat conference, focusing on advancements in cybersecurity products and services. Several companies are leveraging AI to enhance their security offerin…
Horizon3, an AI-powered cybersecurity firm specializing in detecting and mitigating AI-driven attacks, has raised $250 million in a Series E funding round. This significantly increases the company’s valuation to $2 billi…
An attacker exploited a critical vulnerability (CVE-2026-48558) in SimpleHelp’s OpenID Connect (OIDC) flow to deploy the TaskWeaver and Djinn Stealer malware. This allowed for unauthorized access to authenticated ‘Techni…
A critical vulnerability (CVE-2026-20230) in Cisco Unified Communications Manager (CUCM) has been rapidly weaponized by attackers within 24 hours of a proof-of-concept release. The SSRF flaw allows unauthenticated remote…
A critical vulnerability (CVE-2026-48558) in SimpleHelp remote management software allows unauthorized users to create privileged technician accounts via OpenID Connect (OIDC) authentication. This flaw, combined with spe…
A critical command injection vulnerability (CVE-2026-42271) in BerriAI’s LiteLLM has been actively exploited in the wild. The flaw, combined with a separate Starlette vulnerability (CVE-2026-48710), allows for unauthenti…