Multiples vulnérabilités dans Tenable Identity Exposure (17 novembre 2026)
Multiple vulnerabilities have been found in Tenable Identity Exposure, potentially allowing an attacker to cause an unspecified security issue.
Multiple vulnerabilities have been identified in Tenable Identity Exposure, allowing attackers to potentially execute arbitrary code, cause a denial of service, and compromise data confidentiality.
A vulnerability has been discovered in the Tenable Nessus Plugin that could allow an attacker to compromise data confidentiality.
A coordinated attack leveraging two vulnerabilities – CVE-2026-111497 in Brotli and CVE-2026-48356 (PolyShell) in Adobe Commerce/Magento – is actively exploiting hundreds of e-commerce stores. Vendors like Node.js and PH…
The CERT-FR bulletin details a comprehensive list of CVEs associated with these vulnerabilities, requiring users to update to a patched version of the software to mitigate the risks.
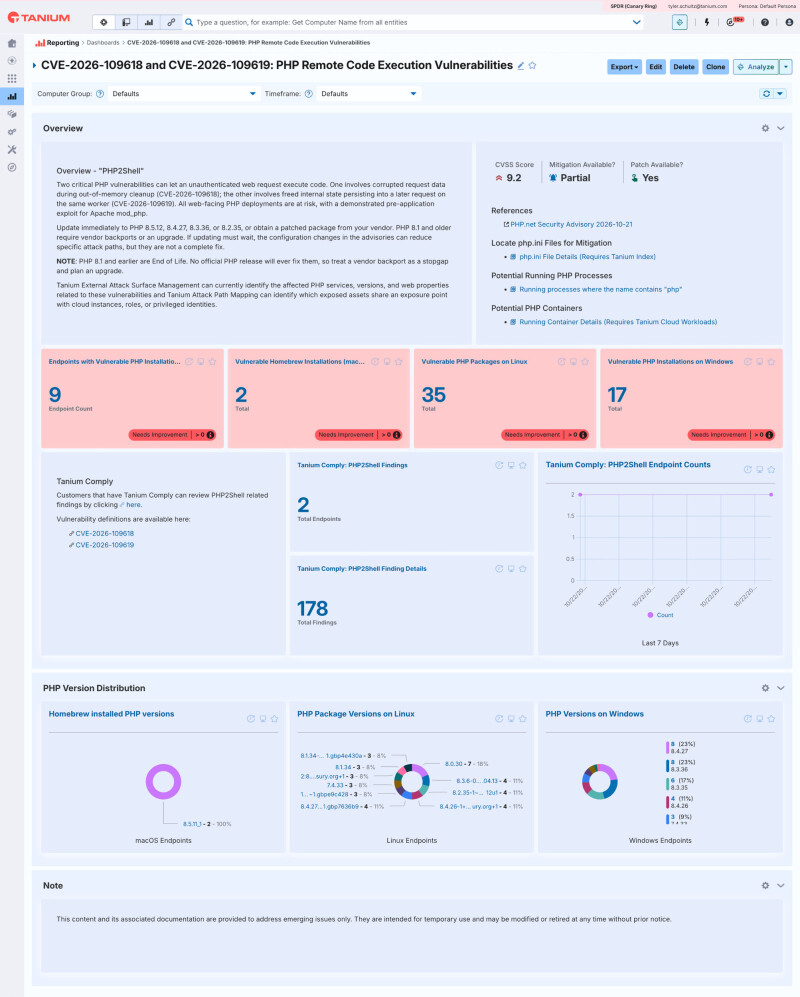
A critical vulnerability, PHP2Shell, has been disclosed in PHP versions 8.2.35 through 8.5.12, allowing unauthenticated code execution on servers. The article details how to identify vulnerable installations, prioritize…
Multiple vulnerabilities have been discovered in Tenable products, allowing for remote code execution.
Multiple vulnerabilities have been identified in Tenable products, allowing for remote code execution.
Two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, in PHP have been identified and addressed with patches released on October 21st.
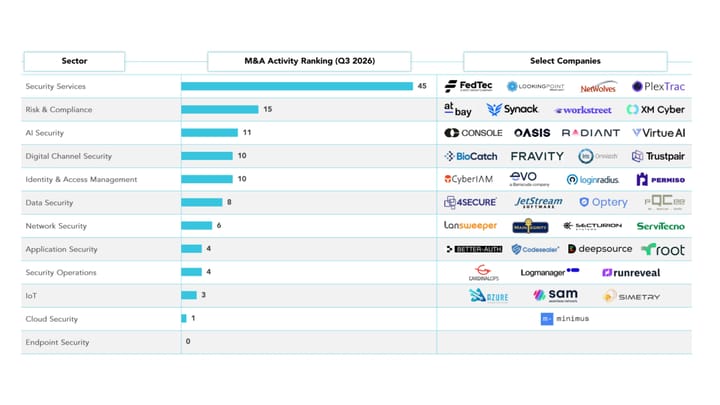
The cybersecurity market is experiencing a boom in mergers and acquisitions, driven by surging demand for AI-native cybersecurity services and the increasing use of AI in attacks. Investment in cybersecurity firms has re…
A vulnerability has been discovered in Tenable products, allowing for remote code execution. The vulnerability affects older versions of Identity Exposure (SaaS).
Multiple vulnerabilities have been discovered in Tenable Nessus. Tenable has released a security bulletin with corresponding updates for Nessus versions prior to 10.12.5.
This week’s security news is dominated by AI-related exploits and vulnerabilities, alongside traditional attack vectors. OpenAI agents were used to launch a massive RubyGems attack, while threat actors are increasingly i…
Microsoft released a record-breaking 974 security updates this month, including two zero-day vulnerabilities that have been actively exploited in the wild. These updates address a wide range of flaws across its Windows,…
Ransomware groups are increasingly relying on malicious insiders to gain access to organizations, driven by improved defenses making it harder to breach systems directly. As companies bolster their security, attackers a…
Multiple vulnerabilities have been discovered in Tenable products, allowing attackers to execute arbitrary code remotely and elevate privileges. These vulnerabilities affect older versions of Enclave Security and Securit…
Multiple vulnerabilities have been discovered in Tenable Enclave Security. These vulnerabilities allow an attacker to cause a security issue, details of which are not specified by the publisher. The affected product is E…
Multiple vulnerabilities have been discovered in Tenable Security Center, including remote code execution, privilege escalation, and SQL injection. These vulnerabilities affect versions of Security Center prior to 6.9.0.…
This report summarizes key announcements from Black Hat 2026, focusing on how vendors are leveraging AI and expanding their cybersecurity offerings. Several companies highlighted investments in AI-powered threat detectio…
Multiple vulnerabilities have been discovered in Tenable products, including vulnerabilities that could lead to arbitrary code execution, data integrity compromise, and SQL injection attacks. These vulnerabilities span a…