TP-Link Sued by Four More U.S. States Over Router Security and China Ties
The states are seeking a court order, surrender of profits, and a mandate for TP-Link to disclose its supply chain and privacy policies.
15 article(s) in our index mention this organisation.
The states are seeking a court order, surrender of profits, and a mandate for TP-Link to disclose its supply chain and privacy policies.
Four US states have filed lawsuits against TP-Link, accusing the router maker of misleading consumers about its security and ties to China. TP-Link has denied the allegations, calling them ‘baseless’ and stating that its…
US state attorneys general are suing TP-Link, alleging deceptive marketing practices and concealment of its reliance on Chinese suppliers and manufacturing. The FCC has already implemented restrictions on new foreign-pro…
A new Linux malware strain, dubbed ‘ClingSTUN,’ is exploiting a growing list of vulnerabilities in IoT devices to establish a persistent foothold on enterprise networks. Researchers have identified at least 24 vulnerabil…
A Linux backdoor, dubbed ClingSTUN, is abusing the STUN protocol to exploit dozens of vulnerabilities and establish a backconnect proxy.
This week’s cybersecurity news highlights a range of threats, from ransomware development and criminal activity to vulnerabilities in popular software and AI systems. A Ukrainian ransomware developer received a 13-year p…
A new Linux botnet, dubbed Evooo1Bot, leveraging Mirai's code, is actively exploiting vulnerabilities in internet-facing devices to turn them into SOCKS5 proxies. The botnet utilizes a range of capabilities including enc…
Researchers at Forescout discovered 15 vulnerabilities within TP-Link's ZTP (Zero-Touch Provisioning) ecosystem, primarily within their Omada networking devices. These vulnerabilities expose organizations to significant…
Researchers at Forescout discovered 15 vulnerabilities in TP-Link’s Omada networking ecosystem’s zero-touch provisioning (ZTP) system, allowing attackers to potentially take over entire networks by chaining together thes…
This week’s cybersecurity recap highlighted a concerning trend of AI-powered exploit generation, alongside a series of high-impact security incidents. A vulnerability in Coldcard hardware wallets led to an $88.6 million…
A new botnet, RustDuck, is leveraging Rust programming to hijack routers, IP cameras, and servers for DDoS attacks. Developed by QiAnXin's XLab, the botnet utilizes a two-stage approach, exploiting vulnerabilities in dev…
Cisco Talos has disclosed multiple vulnerabilities across several popular products, including TP-Link routers, Adobe Photoshop, OpenVPN, and Norton VPN. These vulnerabilities range from buffer overflows and OS command in…
A Brazilian DDoS protection firm, Huge Networks, was found to be running a botnet that launched massive DDoS attacks against Brazilian ISPs. This activity stemmed from a security breach in January 2026 that compromised t…
This report details an ongoing attempt to exploit CVE-2023-33538, a vulnerability in older TP-Link Wi-Fi router models (TL-WR940N v2/v4, TL-WR740N v1/v2, TL-WR841N v8/v10). Automated scans, utilizing Mirai-like malware p…
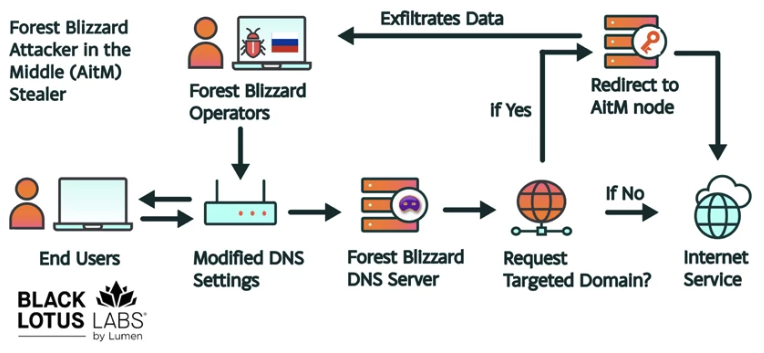
Russian military intelligence, operating under the ‘Forest Blizzard’ (APT28/Fancy Bear) moniker, has been conducting a sophisticated cyber espionage campaign targeting over 18,000 routers globally. The attackers exploite…