ransomware
Social Engineering Detection Moves Into the Live Conversation
Despite significant investment in security awareness training, social engineering remains a highly effective attack vector.
High
An affiliate group of ALPHV, BlackCat Gang (Mandiant) UNC3944 is a financially motivated threat cluster that has persistently used phone-based social engineering and SMS phishing campaigns (smishing) to obtain credentials to gain and escalate access to victim organizations. At least some UNC3944 threat actors appear to operate in underground communities, such as Telegram and underground forums, which they may leverage to acquire tools, services, and/or other support to augment their operations. This activity overlaps with activity that has been reported in open sources as '0ktapus,' 'Scatter Swine,' and 'Scattered Spider.' Since 2022 and through early 2023, UNC3944 appeared to focus on accessing credentials or systems used to enable SIM swapping attacks, likely in support of secondary criminal operations occurring outside of victim environments. However, in mid-2023, UNC3944 began to shift to deploying ransomware in victim environments, signaling an expansion in the group's monetization strategies. These changes in their end goals signal that the industries targeted by UNC3944 will continue to expand; Mandiant has already directly observed their targeting broaden beyond telecommunication and business process outsourcer (BPO) companies to a wide range of industries including hospitality, retail, media and entertainment, and financial services. Around July 2025, ShinyHunters teamed up or merged with Scattered Spider. They share their Telegram channel also with Lapsus$, so they may all work together now – see the DataBreaches.net references in the Information section under ShinyHunters.
Despite significant investment in security awareness training, social engineering remains a highly effective attack vector.
Ransomware groups are increasingly relying on malicious insiders to gain access to organizations, driven by improved defenses making it harder to breach systems directly. As companies bolster their security, attackers a…
A significant trend in cyberattacks is the increasing reliance on compromised identities rather than exploiting technical vulnerabilities. Nearly 90% of Unit 42 investigations involved identity weaknesses, with 65% of in…
Maksim Silnikau, the mastermind behind the Ransom Cartel ransomware operation, has been sentenced to 16 years in prison for his role in a multi-year criminal scheme targeting organizations across the US and abroad. The o…
A recent attack against the author’s wireless account highlights a growing trend of coordinated identity attacks, moving beyond simple authentication failures. The attacker leveraged social engineering, stolen credential…
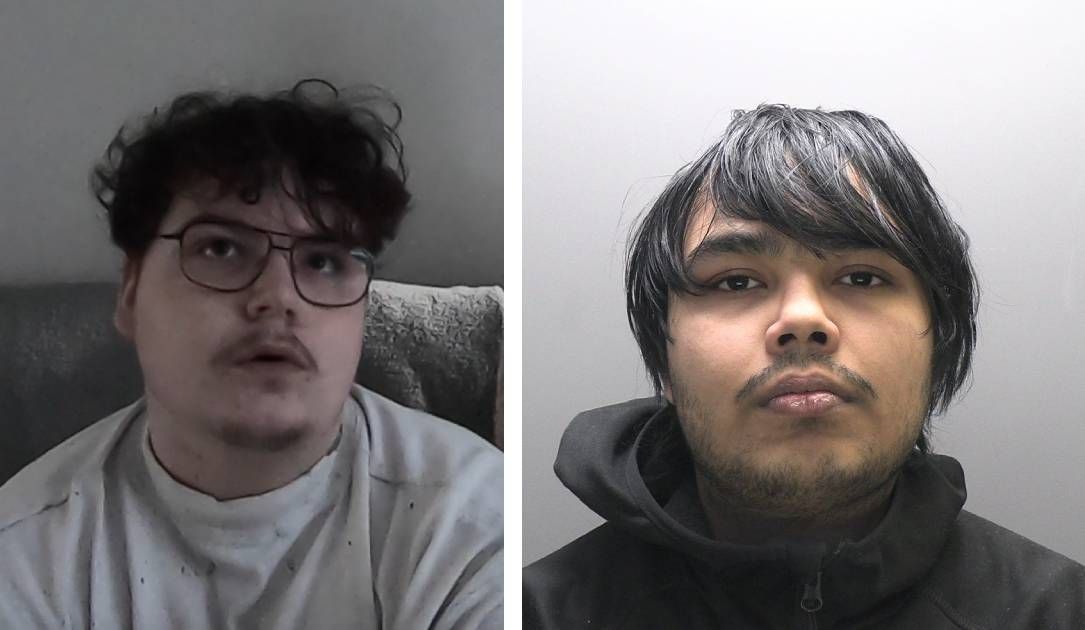
Two young British hackers, Owen Flowers and Thalha Jubair, were convicted and sentenced to five and a half years for a sophisticated attack on Transport for London (TfL), resulting in significant disruption and financial…
Two members of the Scattered Spider cybercrime group, Thalha Jubair and Owen Flowers, were sentenced to prison in the UK for their role in a 2024 attack on Transport for London, resulting in significant financial losses.…
Two members of the Scattered Spider cybercrime group, Thalha Jubair and Owen Flowers, have been sentenced to over five years in prison for their role in a 2024 attack against Transport for London (TfL). The attack caused…
A threat actor, linked to the O-UNC-066 group (affiliated with The Com/Scattered Spider), is using a sophisticated, operator-controlled phishing kit to trick users into enrolling fake Microsoft Entra passkeys, gaining un…
This week's ThreatsDay highlights a diverse range of cyber threats, from global fraud operations and ransomware tool overlaps to sophisticated social engineering attacks and vulnerabilities in popular software. Key event…
U.S. prosecutors have linked an alleged Scattered Spider hacker, Peter Stokes, to a luxury jewelry retailer breach through a persistent Windows device ID. Stokes, a dual U.S.-Estonian citizen, was extradited from Finland…
This week’s security recap highlighted several concerning trends, including a disruption of the NetNut residential proxy network used for botnet operations, a fake Proof-of-Concept (PoC) malware targeting vulnerability r…